Converting Security Assessment Findings into Defensible Remediation Roadmaps
When a comprehensive security assessment concludes, compliance officers, managing partners, and IT directors are often handed a dense artifact: dozens of pages detailing vulnerabilities, misconfigurations, and compliance gaps. For small and mid-sized businesses (SMBs), the sheer volume of findings can create operational paralysis. When every finding is marked as critical by automated scanning tools, leadership struggles to answer a fundamental business question: Where do we invest our finite time and engineering budget first?
Without a structured prioritization methodology, organizations frequently fall into one of two traps. Either they attempt to fix everything at once—stalling business initiatives and exhausting IT teams—or they engage in checklist theater, rapidly checking off low-hanging fruit to satisfy an immediate reporting deadline without addressing underlying architectural risk.
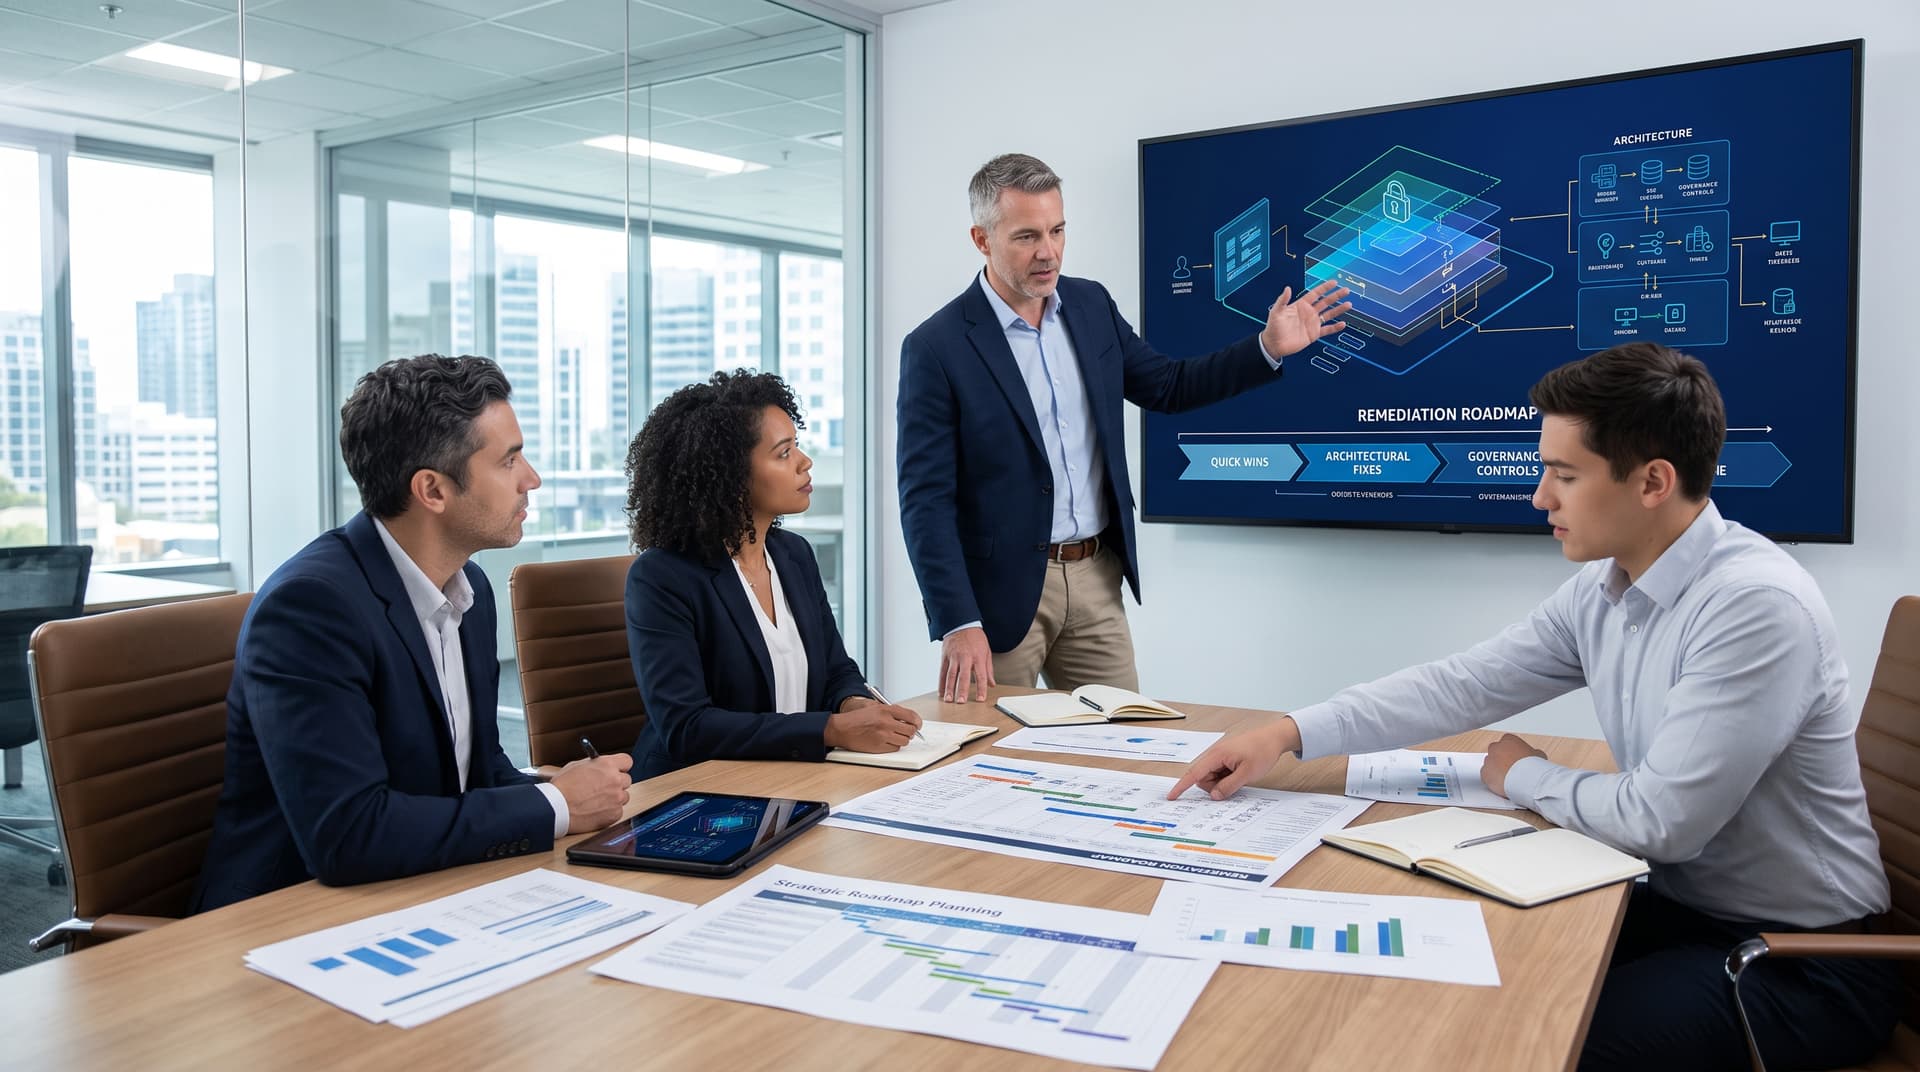
Through expert security consulting, organizations can transform overwhelming assessment data into a phased, defensible risk roadmap. By categorizing findings into quick wins, structural architectural upgrades, and formal governance controls, SMBs achieve immediate risk reduction while building an audit-ready posture.
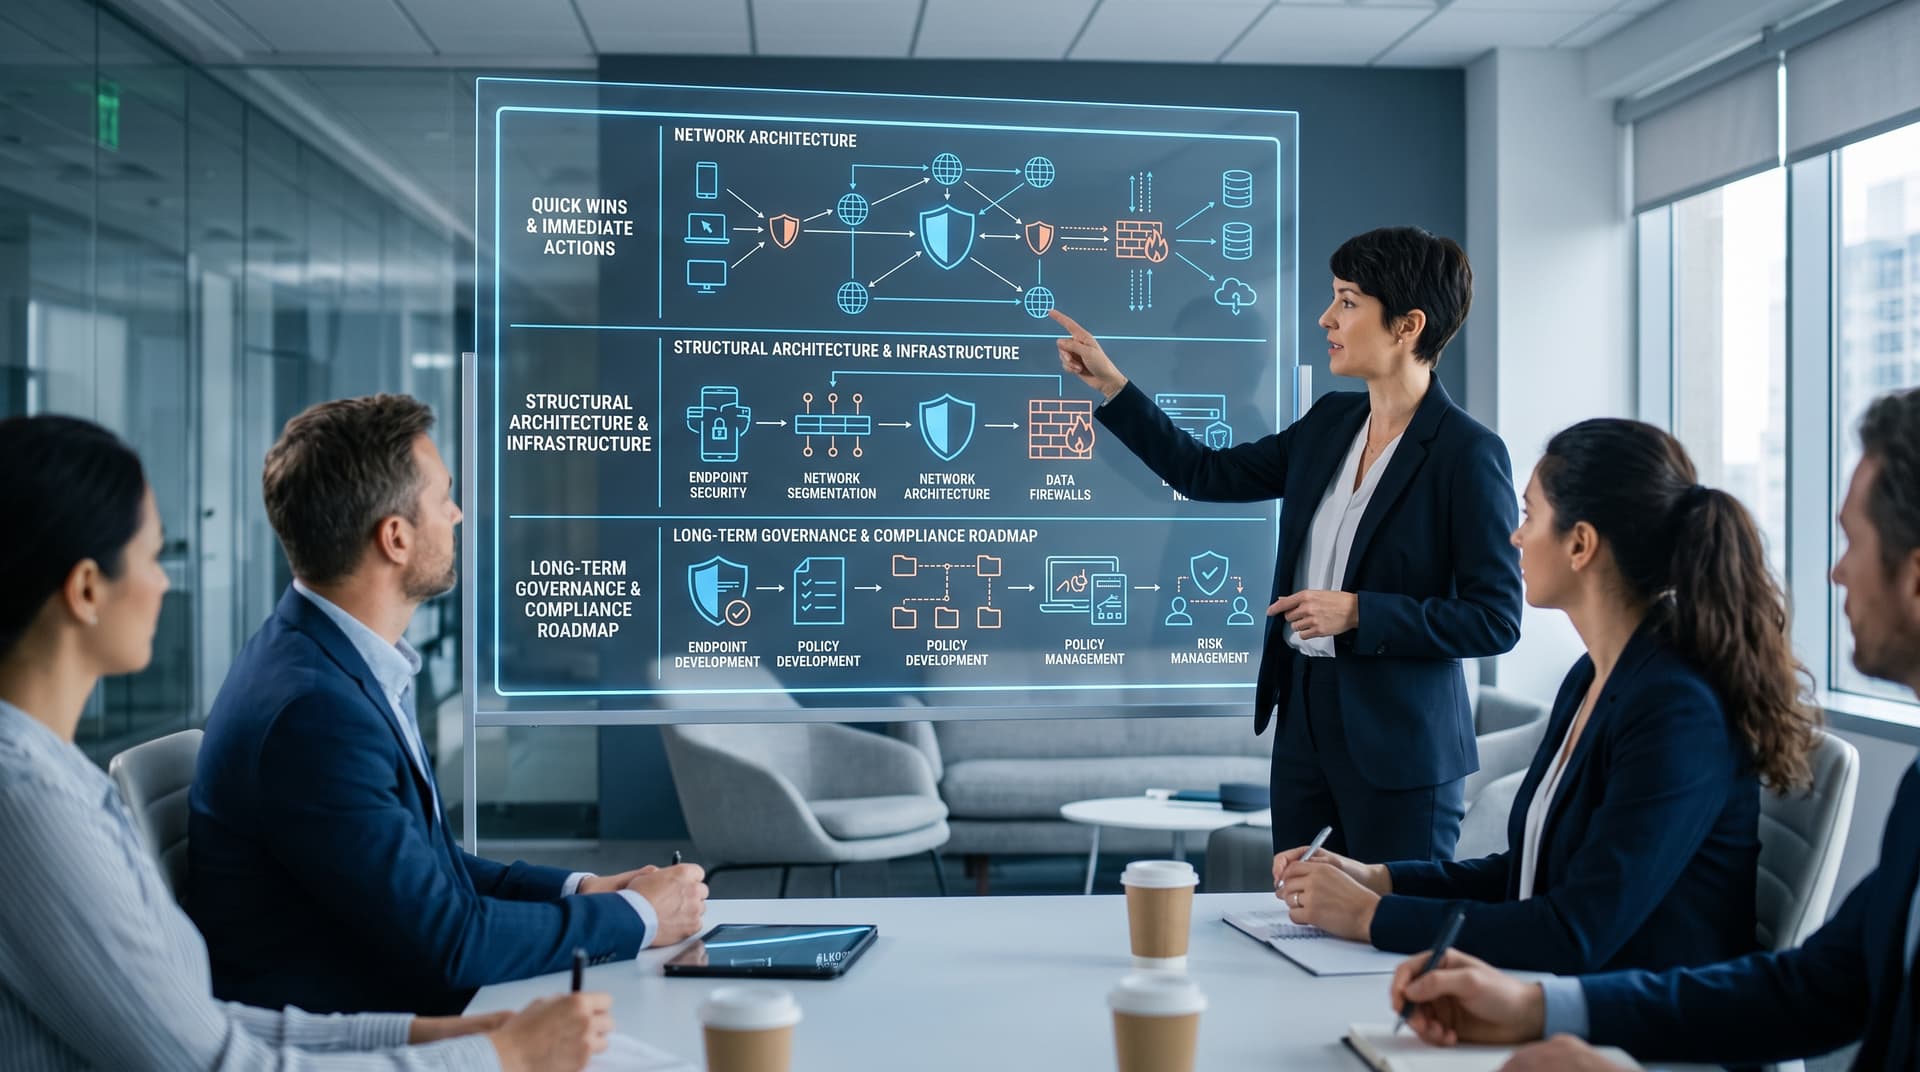
The Three-Tier Prioritization Framework
A practical risk roadmap organizes findings based on exploitability, operational friction, implementation cost, and business impact. Rather than treating all vulnerabilities as equal, SMBs should sequence work across three execution windows.
Tier 1: Immediate Quick Wins (0–30 Days)
Quick wins are tactical configuration adjustments and credential hygiene fixes that deliver massive risk reduction with minimal operational disruption and zero added licensing costs. These items directly eliminate common attack vectors targeted by automated threat scripts and opportunistic attackers.
Key Tier 1 actions typically include:
- Enforcing Multi-Factor Authentication (MFA): Mandating phishing-resistant MFA across all identity providers, VPNs, and remote access endpoints.
- Disabling Legacy Protocols: Terminating outdated authentication methods (such as NTLMv1 or basic authentication) that bypass modern conditional access policies.
- Eliminating Orphaned Accounts: Deprovisioning dormant contractor and former employee accounts discovered during identity audits.
- Applying Critical External Patches: Remediation of publicly accessible vulnerabilities on firewalls, edge routers, and web application portals.
To quickly benchmark your identity and perimeter exposure before establishing your roadmap, run the free Microsoft 365 Security Snapshot to identify high-risk tenant configurations.
Tier 2: Structural Architectural Upgrades (30–90 Days)
Structural fixes address systemic technical debt and foundational infrastructure vulnerabilities. Unlike quick wins, these projects require capital allocation, solution design, cross-departmental coordination, and planned maintenance windows.
Key Tier 2 initiatives include:
- Zero Trust Network Segmentation: Moving away from flat network topologies to isolate payment systems, production databases, and internal user workstations.
- Privileged Access Management (PAM): Removing local administrative rights from end-user workstations and establishing just-in-time (JIT) access for system administrators.
- Immutable Backup Architecture: Hardening data backup infrastructure against ransomware encryption by deploying air-gapped or write-once-read-many (WORM) storage controls.
- Endpoint Detection and Response (EDR) Optimization: Replacing legacy signature-based antivirus with behavior-driven EDR agents backed by 24/7 Security Operations Center (SOC) monitoring.
Before undertaking deep architectural changes, evaluating your storage resiliency using the Ransomware Readiness Scorecard provides objective benchmarks for recovery capability.
Tier 3: Governance, Policy, and Continuous Operations (90–180+ Days)
Governance controls ensure technical fixes remain durable over time. Without governance, configuration drift and employee turnover inevitably erode security gains. Tier 3 projects embed security into standard business workflows.
Key Tier 3 initiatives include:
- Formal Policy Creation and Revision: Writing and enforcing clear Incident Response Plans (IRP), Vendor Risk Management (VRM) standards, and Data Classification policies.
- Third-Party Risk Assessments: Auditing cloud vendors, software providers, and managed service providers for downstream security compliance.
- Security Awareness Training & Simulation: Establishing routine phishing simulations and role-based training for high-risk personnel, such as finance and human resources teams.
- Regular Advisory Oversight: Retaining fractional vCISO services to review emerging threats and maintain continuous alignment with business objectives.
Escaping "Checklist Theater": Building Audit-Ready Evidence
One of the most frequent failures in SMB compliance management is checklist theater—the practice of temporarily toggling settings or acquiring security tools solely to pass an annual assessment, without maintaining operational proof of enforcement.
Regulators, cyber insurance underwriters, and enterprise buyers no longer accept static self-attestation questionnaires. Modern auditors demand audit-grade evidence: verifiable, time-stamped, and historical artifacts demonstrating that controls operate continuously.
What Visual & Systemic Evidence Looks Like
To satisfy external auditors and cyber insurance providers, evidence collection must be integrated into daily engineering and IT operations:
- Policy vs. Practice: A policy requiring quarterly access reviews is insufficient without exported CSV reports signed off by data owners.
- Configuration Snapshots: Screenshots or automated API log exports showing active baseline configurations across cloud environments (e.g., AWS Security Hub or Microsoft Defender baselines).
- Centralized Log Retention: Centralized SIEM logs verifying log collection across domain controllers, firewalls, and SaaS platforms retained for at least 90–365 days.
- Remediation History: Change management tickets showing the lifecycle of a vulnerability from initial discovery during an assessment to successful deployment and validation testing.
Takeaway: Checklist theater satisfies a point-in-time questionnaire but fails during an incident investigation or rigorous regulatory audit. Defensible security relies on repeatable processes backed by immutable log evidence.
Illustrative Remediation & Evidence Matrix
The following matrix illustrates how SMB leadership can map security assessment findings to prioritized execution windows and evidence requirements:
| Finding Category | Example Defect Identified | Remediation Phase | Target Timeline | Required Audit Evidence |
|---|---|---|---|---|
| Identity & Access | MFA missing for remote access | Tier 1: Quick Win | Days 1–14 | Identity tenant policy export showing enforced MFA for 100% of users |
| Network Infrastructure | Flat corporate network; internal subnets unsegmented | Tier 2: Structural Fix | Days 30–75 | Network topology diagrams, firewall rule exports, sub-interface routing tables |
| Data Protection | Unencrypted server backups stored on network share | Tier 2: Structural Fix | Days 45–90 | Immutable storage log verification, successful restore test reports |
| Vendor Governance | Core SaaS vendor lacks SOC 2 Type II assessment | Tier 3: Governance | Days 90–120 | Completed vendor risk scorecards, third-party SOC 2 review documentation |
| Incident Response | Outdated Incident Response Plan; no tabletop exercise | Tier 3: Governance | Days 120–150 | Executed IRP document, signed tabletop exercise post-mortem report |
Note: Framework values are an illustrative execution heuristic designed for operational planning.
The Role of Strategic Security Consulting in Remediation
Internal IT teams in growing companies are frequently overloaded maintaining day-to-day operations, end-user support, and infrastructure management. Expecting internal personnel to independently digest complex assessment reports, design architectural fixes, and generate compliance artifacts often leads to burnout and delayed remediation.
Engaging specialized security consulting provides SMBs with seasoned expertise without the overhead of hiring a full-time Chief Information Security Officer (CISO). External advisors bring key advantages:
- Objective Risk Assessment: Prioritizing issues based on actual threat actor behavior rather than default vendor severity scores.
- Cross-Industry Perspective: Applying proven remediation tactics distilled from hundreds of client environments.
- Executive Communication: Translating technical vulnerabilities into financial and operational risk metrics that resonate with board members and managing partners.
- Audit Facilitation: Acting as a bridge between technical teams and external auditors to ensure evidence submissions meet compliance criteria.
Accelerate Your Security Roadmap
A security assessment is only as valuable as the execution roadmap it produces. By converting raw technical findings into prioritized, audit-ready operational phases, your organization can efficiently reduce risk, satisfy compliance mandates, and maintain business momentum.
Whether you need an initial objective assessment or strategic guidance implementing recommendations from a recent audit, Bitscaled delivers tailored advisory services for growing enterprises.
Request a scoped security assessment from Bitscaled today to build your defensible risk roadmap.